Showing posts with label Cyber Attack. Show all posts

Cyber Strikes on U.S. Water Supply Linked to Iran

Cyber Strikes on U.S. Water Supply Linked to Iran

Iranian-affiliated hackers have widened their attacks on U.S. water systems in 2026, exploiting weak security in control systems and causing operational disruptions across multiple states. Federal agencies including the EPA, FBI, CISA, and NSA have confirmed that these attacks directly threaten public health and community resilience.

According to The New York Times, cyberattacks on U.S. water systems have spread to at least seven states, and experts warn the problem could be even bigger. Authorities are rushing to protect the nation’s water supply, with evidence pointing to hackers linked to Iran

What Happened

  • Joint Advisory (April 2026): The EPA, FBI, CISA, and NSA issued a nationwide warning about Iranian-affiliated cyber actors targeting drinking water and wastewater systems.
  • Attack Escalation (March–July 2026): Iranian APT groups linked to the IRGC began exploiting programmable logic controllers (PLCs) in water, energy, and government infrastructure.
  • Methods Used: Hackers accessed internet-exposed PLCs (Siemens, Allen-Bradley, Unitronics) using default or weak passwords, wiping configurations and tampering with sensors.
  • Impact: Disruptions included loss of water pressure, flooding, boil water notices, and manual system resets.
The reason U.S. water systems are vulnerable to cyberattacks is because many of their control devices, like programmable logic controllers (PLCs) and supervisory control systems, are directly connected to the internet without proper safeguards. Hackers exploit weak passwords, outdated software, and exposed remote access points to disrupt operations.

The U.S. water supply is vulnerable because automation and remote access were added without strong cybersecurity protections. Smaller utilities, with limited budgets, are especially at risk. Hackers don’t need advanced tools—just poor cyber hygiene is enough to cause loss of water pressure, flooding, or unsafe drinking water.

Why It Matters

  • Public Health Risk: Cyberattacks can disrupt water treatment, potentially introducing contaminants into drinking water.
  • Critical Infrastructure Vulnerability: Smaller utilities with limited budgets and outdated systems are the most exposed.
  • Geopolitical Context: Analysts assess these attacks as retaliation amid heightened U.S.–Iran tensions, showing Iran’s ability to cause real-world disruption without advanced exploits.

Government Response

  • EPA & FBI Guidance: Utilities are urged to adopt cybersecurity best practices, report incidents immediately, and work with investigators.
  • Support Programs: The EPA offers free cybersecurity assessments, technical assistance, and training to help even small utilities strengthen defenses.
  • National Cyber Strategy: The U.S. is imposing costs on malicious actors while building resilience across critical infrastructure.

Attack Overview

SectorImpactMethods UsedNotes
Water systemsBoil water notices, flooding, manual resetsWeak/default PLC credentialsHighest number of confirmed incidents
Energy sectorLimited disruption, reconnaissancePLC exploitationNo full shutdown yet
Government servicesTraffic & municipal systems disruptedInternet-exposed HMIsOpportunistic targeting

Defensive Measures for Utilities

  • Remove internet-exposed control systems where possible.
  • Enforce strong, unique credentials for PLCs and SCADA systems.
  • Apply patches and updates to legacy infrastructure.
  • Report incidents promptly to FBI and CISA.

Big Picture

The widening scope of Iranian-linked hacks underscores systemic vulnerabilities in U.S. water infrastructure. While large metropolitan systems are better defended, smaller community utilities remain prime targets. These attacks highlight the urgent need for cyber hygiene, federal support, and coordinated resilience measures to safeguard America’s lifeline services.

Massive Browser-Based RTO Scam Targets Indian Vehicle Owners; Over 36 Fake e-Challan Domains Discovered

Massive Browser-Based RTO Scam Targets Indian Vehicle Owners; Over 36 Fake e-Challan Domains Discovered

  • Sophisticated Phishing Campaign Uses Localized Infrastructure Including Reliance Jio Numbers and State Bank Account Links; Shared Infrastructure Also Targets BFSI and Logistics Sectors
Cyble Research and Intelligence Labs (CRIL) has uncovered a large-scale browser-based phishing campaign targeting Indian vehicle owners through fake e-Challan portals. The sophisticated operation, which represents an evolution from previous malware-driven attacks, leverages over 36 fraudulent domains and exploits trust in Regional Transport Office (RTO) services to harvest banking credentials.

The investigation, which aligns with recent warnings from mainstream media including Hindustan Times, reveals an active and ongoing campaign using localized infrastructure to enhance credibility and maximize victim impact.

"This campaign demonstrates a pivot from the previously observed Android malware use to browser-based fraud, which significantly lowers the technical barriers and expands the pool of potential victims," said Daksh Nakra, Senior Manager of Research and Intelligence at Cyble. "The use of Indian mobile numbers registered with popular telecom operators and linked to State Bank of India accounts shows how attackers deliberately exploit trust in familiar institutions to increase success rates."

Campaign Overview and Attack Flow

Multi-Stage Phishing Operation

  • Victims receive SMS messages claiming overdue traffic fines.
  • Urgency created through threats of license suspension, court summons, and legal proceedings.
  • Messages contain shortened URLs mimicking legitimate e-Challan domains.
  • Victims are led to cloned government portals.

Key Technical Findings:

Dynamic Challan Fabrication

  • Portal generates realistic-looking violation records regardless of input.
  • Displays modest fine amounts (typically INR 590) with near-term expiration dates.
  • No backend verification occurs—purely psychological manipulation.
  • Replicates official MoRTH branding and NIC insignia.

Card Data Harvesting

  • Payment pages restrict options to credit/debit cards only.
  • Avoids traceable UPI and net banking transactions.
  • Collects full card details including CVV and expiry dates.
  • Claims processing through Indian banks.
  • Accepts repeated submissions, transmitting all data to attacker backend.

Localized Infrastructure for Enhanced Credibility

  • SMS sent from Indian mobile number registered with Reliance Jio Infocomm Limited.
  • Phone number linked to State Bank of India account.
  • Combination of local telecom carrier and public-sector bank association increases perceived legitimacy.

Shared Fraud Infrastructure Uncovered

  • Over 36 phishing domains impersonating e-Challan services.
  • Additional targets: HSBC-themed payment lures (BFSI sector).
  • Logistics company impersonation: DTDC, Delhivery.
  • Consistent UI patterns and payment-harvesting logic across campaigns.

Secondary Infrastructure

  • Multiple domains mimicking Parivahan services.
  • Automatically generated phishing domains suggesting rotation techniques.
  • Designed to evade takedowns and blocklists.
  • Same operational flow as primary campaign.

Anti-Detection Measures:

  • Content originally authored in Spanish, translated via browser prompts.
  • Indicates reuse of phishing templates across regions.
  • Browser-based warnings (Microsoft Defender) ignored due to urgency cues.
  • Domain generation techniques for infrastructure resilience.

Multi-Sector Risk:

  • Government service users (e-Challan, Parivahan).
  • Banking customers (HSBC-themed lures).
  • E-commerce users (DTDC, Delhivery impersonation).

Critical Recommendations

  • Never click links in unsolicited SMS claiming traffic violations.
  • Always verify fines directly through official government portals (parivahan.gov.in).
  • Scrutinize domains carefully—look for spelling variations and unusual TLDs.
  • Be suspicious of payment pages accepting only credit/debit cards.
  • Report suspicious messages to cybercrime authorities immediately.
Complete technical analysis, indicators of compromise (IoCs), MITRE ATT&CK mappings, and detection guidance are available in the full blog post here.

IoCs have been published to Cyble's GitHub repository for immediate integration into security platforms and threat intelligence feeds.

About Cyble

Cyble is a global AI-powered threat intelligence company providing organizations with real-time visibility into cyber threats through advanced research, dark web monitoring, attack surface management, and comprehensive security solutions. Cyble's platform delivers actionable intelligence enabling security teams to detect, respond to, and prevent cyberattacks before they cause significant damage.

For more information, visit www.cyble.com.

Cyber Interference Hits Delhi Airport Navigation Systems; Probe Launched

Cyber Interference Hits Delhi Airport Navigation Systems; Probe Launched

Delhi Airport recently faced a cyberattack attempt involving GPS spoofing signals. Pilots reported false navigation data, but backup systems and contingency procedures ensured flight safety. The government has confirmed the incident and launched investigations.

The Indian government and aviation authorities have officially confirmed the GPS spoofing incident near Delhi Airport. Civil Aviation Minister Ram Mohan Naidu acknowledged it in Parliament, and the aviation regulator DGCA issued directives to airlines and pilots to report such cases promptly.

The Ministry of Civil Aviation told Parliament that flights near Delhi and other major airports faced GPS spoofing and GNSS interference over the past year. Minister Ram Mohan Naidu confirmed that pilots were forced to switch to backup landing modes when navigation data was compromised.  

What Happened at Delhi Airport

  • Type of attack: GPS spoofing — fake satellite signals were transmitted to mislead aircraft navigation systems about their actual position.
  • Impact: Pilots received incorrect data, including false aircraft positions and misleading terrain warnings.
  • Scope: Delhi’s Indira Gandhi International Airport was among several major airports (including Mumbai and Bengaluru) that detected such signals.
  • Government response: Civil Aviation Minister Ram Mohan Naidu confirmed in Parliament that GPS spoofing and GNSS interference attempts had occurred over the past year.
  • Safety measures: Conventional navigation systems (like Instrument Landing Systems and radar) were used to override spoofed signals, ensuring no accidents occurred.

What “Switching to Backup Landing Modes” Means

Cyber Interference Hits Delhi Airport Navigation Systems; Probe Launched
When GPS spoofing compromised the aircraft’s satellite navigation data, pilots could no longer trust the primary GNSS/GPS guidance for approach and landing. In such cases, they revert to backup landing modes, which are older but highly reliable systems:
  • Instrument Landing System (ILS): Uses radio beams from ground transmitters to guide aircraft precisely down to the runway. It’s the gold standard backup for low‑visibility landings.
  • VOR/DME (VHF Omnidirectional Range / Distance Measuring Equipment): Provides position and distance information using ground‑based radio signals. Pilots can navigate and align with the runway without GPS.
  • Radar Vectoring by Air Traffic Control (ATC): Controllers give pilots heading and altitude instructions to safely guide them to final approach.
  • Visual Flight Rules (VFR): If weather is clear, pilots may rely on direct visual cues to land safely.

After Effects 

  • GPS spoofing disrupted the “modern” navigation layer.
  • Pilots had to fall back on conventional radio‑based systems that are immune to satellite signal manipulation.
  • This ensured flight safety despite compromised GPS data.

Think of it like driving with a GPS app that suddenly shows you on the wrong road. Instead of following the faulty GPS, you switch to road signs and landmarks — older but trustworthy guidance — to reach your destination safely.

Pilots switched to ground‑based navigation aids and ATC guidance when GPS signals were spoofed, ensuring safe landings despite compromised satellite data.

Investigations Underway

  • NSA Ajit Doval’s office has launched a probe into the Delhi incident, treating it as a national security matter.
  • Civil Aviation Ministry acknowledged the cyberattack attempt and assured Parliament that contingency procedures are in place.
  • International parallels: Similar GPS spoofing incidents have been reported globally, especially near conflict zones, raising concerns about aviation cybersecurity.

Risks & Challenges

  • Operational disruption: Over 400 flights across India were reportedly disrupted last month due to navigation interference.
  • National security: GPS spoofing can be used to misdirect aircraft, posing risks not just to safety but also to defense operations.
  • Cyber resilience gap: India’s aviation systems rely heavily on satellite navigation, making them vulnerable to spoofing unless robust countermeasures are deployed.

Quick Comparison: GPS Spoofing vs. Traditional Cyberattacks

Feature GPS Spoofing (Delhi Case) Traditional Cyberattack (e.g., ransomware)
Target Aircraft navigation systems IT infrastructure, servers, data
Method Fake satellite signals Malware, phishing, unauthorized access
Impact Misleading flight paths, terrain warnings Data theft, system shutdown, ransom demands
Detection Pilot reports, backup system alerts Security software, forensic analysis
Countermeasures Conventional navigation systems, contingency procedures Firewalls, backups, patching

Key Takeaway

Delhi Airport’s navigation systems were indeed under attack via GPS spoofing. Flights remained safe thanks to backup systems, but the incident highlights growing cyber threats to aviation. India is now investigating the matter at the highest levels, signaling the seriousness of such interference.

Voice Phishing Breach at Cisco: ShinyHunters Suspected in CRM Data Heist

Voice Phishing Breach at Cisco: ShinyHunters Suspected in CRM Data Heist

Cisco has confirmed a targeted voice phishing (vishing) attack that compromised user profile data stored in a third-party cloud-based Customer Relationship Management (CRM) system. The breach, discovered on July 24, 2025, involved an attacker impersonating a trusted entity over the phone to manipulate a Cisco representative into granting unauthorized access.

Cisco Vishing Attack: What Happened

On July 24, 2025 (GMT+9), Cisco was alerted to a voice phishing (vishing) attack targeting one of its representatives. The attacker impersonated a trusted entity over the phone and successfully manipulated the employee into granting access to a third-party, cloud-based Customer Relationship Management (CRM) system.

What Data Was Compromised

The attacker exported a subset of basic profile information from users who had registered on Cisco.com:
Compromised Data
Full names
Organization names
Physical addresses
Cisco-assigned user IDs
Email addresses
Phone numbers
Account-related metadata (e.g., account creation date)

No passwords, confidential customer data, or proprietary information were accessed.

Cisco’s Response

Cisco took immediate action:
  • Terminated the attacker’s access to the CRM system
  • Launched a full investigation
  • Notified affected users and data protection authorities
  • Confirmed no impact to other CRM instances or Cisco products/services

They also committed to:
  • Re-educating personnel on identifying and preventing vishing attacks
  • Implementing enhanced security measures to prevent recurrence

Broader Context

This breach appears to be part of a larger campaign targeting companies using Salesforce and other CRM platforms. Other victims include Allianz Life, Tiffany & Co., and Qantas. The ShinyHunters extortion group is suspected to be behind these coordinated attacks.

Tata Technologies Faces Ransomware Attack Resulting Temporary Suspension of Some of Its IT Services

Tata Technologies Faces Ransomware Attack Resulting Temporary Suspension of Some of Its IT Services

Tata Technologies recently experienced a ransomware attack that affected some of its IT assets. The attack led to the temporary suspension of certain IT services. However, Tata Technologies confirmed that their client delivery services remained fully functional and unaffected throughout the incident.

The ransomware incident was discovered on January 31, 2025. Tata Technologies did not disclose whether a ransom was demanded or paid.

A detailed investigation is underway in consultation with experts to assess the root cause and take necessary remedial actions.

The company has restored the affected services and launched a detailed investigation to determine the root cause and take necessary remedial actions.

CEO Warren Harris highlighted the importance of increased funding for upskilling initiatives aligned with Industry 4.0 to support India's economic growth.

Tata Technologies emphasized its commitment to maintaining high standards of security and data protection. They are working closely with experts to mitigate any potential risks associated with the attack.

This incident highlights the growing cybersecurity challenges faced by companies, especially in sectors like engineering and technology.

Last December, Deloitte UK was reportedly cyberattacked for whopping 1 TB of sensitive data by ransomware group called Brain Cipher Ransomware.

Last year, Infosys' U.S.-based subsidiary, McCamish Systems, experienced a significant data breach due to a ransomware attack attributed to the LockBit ransomware operation, and data from over 6.078 million individuals was compromised.

Japan Airlines Faces Cyberattack Disrupting More Than 20 Domestic Flights

Japan Airlines Faces Cyberattack Disrupting More Than 20 Domestic Flights

Japan Airlines faced a cyberattack that disrupted more than 20 domestic flights. The attack, which occurred on December 26, 2024, was identified as a denial-of-service (DDoS) attack designed to overwhelm the airline's network with massive data transmissions. Ticket sales for same-day flights were temporarily suspended.

Fortunately, the airline managed to halt the attack and restore its systems within hours, ensuring that flight safety was not compromised.

The cyberattack disrupted both internal and external systems, leading to delays of over 30 minutes for 24 domestic flights. Despite the disruption, Japan Airlines confirmed that no customer data was compromised. The incident highlights the ongoing challenges and vulnerabilities in cybersecurity, especially as Japan strengthens its defense strategies and collaborations with international partners.

Japan Airlines took immediate action by shutting down the affected router to prevent further damage. Systems were restored later in the day, and flights resumed normally by December 27.

This incident is a stark reminder of the importance of robust cybersecurity measures in today's digital age.

In the past year, Japan has experienced several high-profile cyberattacks.To recall, in June 2024 Japanese space agency, JAXA, reported a series of cyberattacks since 2023. Although no critical data related to rockets, satellites, or defense systems was compromised, the agency took steps to bolster its cybersecurity measures.

Last year, a cyberattack paralyzed operations at a container terminal in Nagoya city of Japan, for three days. This incident highlighted the vulnerabilities in Japan's digital infrastructure.

In 2018, Cathay Pacific Airways of America suffered a data breach that compromised the personal data of 9.4 million customers, including credit card information and passport details. The breach continued until May 2020.

These incidents underscore the urgent need for enhanced cybersecurity measures in the aviation industry to protect operations, passenger safety, and organizational reputation.

US Govt's CISA Issues Guidance for Cisco Devices Frequently Targeted by China-affiliated Threat Actors

Us Govt's CISA Issues Guidance for Cisco  Devices Frequently Targeted by China-affiliated Threat Actors

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued specific guidance for network engineers and defenders to patch and secure Cisco network devices in response to the Salt Typhoon cyber-espionage campaign linked to the People's Republic of China (PRC). 

Cisco gear has been frequently targeted by PRC-affiliated threat actors, says the CISA guidance, which is developed in collaboration with other cybersecurity agencies from Australia, Canada, and New Zealand.

The guidance titled "Enhanced Visibility and Hardening Guidance for Communications Infrastructure" is a joint publication by the Cybersecurity and Infrastructure Security Agency (CISA), National Security Agency (NSA), Federal Bureau of Investigation (FBI), Australian Signals Directorate's Australian Cyber Security Centre (ACSC), Canadian Cyber Security Centre (CCCS), and New Zealand's National Cyber Security Centre (NCSC-NZ).

The guide aims to provide best practices for network engineers and defenders to strengthen visibility and harden network devices against cyber threats, particularly those affiliated with the People's Republic of China (PRC).

CISA has provided Cisco-specific advice, including patching vulnerable devices and following best practices outlined in Cisco's IOS XE Hardening Guide and Guide to Securing NX-OS Software Devices.

Enhancing visibility means having detailed insight into network traffic, user activity, and data flow, which helps in quickly identifying threats and vulnerabilities. Hardening involves implementing measures to secure network devices and reduce potential entry points for cyber threats.

Scope of Attacks: The attacks compromised networks of eight telecommunications providers, exfiltrating customer call records and compromising private communications.

The guide includes recommendations such as patching vulnerable devices, monitoring configuration changes, and implementing strong network flow monitoring solutions.

Enhanced Visibility and Hardening Guidance

Patch Vulnerabilities: Ensure all network devices, including routers, switches, and firewalls, are up-to-date with the latest security patches.

Monitor Configuration Changes: Implement comprehensive alerting mechanisms to detect unauthorized changes to network devices. Store configurations centrally and push them to devices.

Network Flow Monitoring: Implement a strong network flow monitoring solution to gain visibility into network traffic and detect anomalies.

Strong Authentication: Use strong passwords and implement two-factor authentication (2FA) to enhance security

End-to-End Encryption: Adopt end-to-end encryption for communications to protect data from interception.

Regular Audits: Conduct regular security audits and penetration tests to identify and address vulnerabilities.

Implementation Steps

Update Systems: Regularly update all network devices and software to the latest versions.

Implement Monitoring Tools: Deploy network monitoring tools to track traffic and detect unusual activities.

Centralize Configurations: Store device configurations centrally and push updates to devices to prevent unauthorized changes.

Enable Alerts: Set up alerts for any configuration changes or unusual activities on network devices.

Use Strong Passwords: Enforce the use of strong, unique passwords for all network devices and accounts.

Implement 2FA: Enable two-factor authentication for accessing critical network devices and systems.

Encrypt Communications: Ensure that all sensitive communications are encrypted end-to-end.

Conduct Audits: Perform regular security audits and penetration tests to identify and fix vulnerabilities.

By following these recommendations, telecommunications providers can significantly enhance their network security and protect against sophisticated cyber-espionage campaigns like Salt Typhoon.

Began in 2022, Salt Typhoon has targeted at least eight U.S. telecommunications providers, including major companies like AT&T, Verizon, and Lumen Technologies. The malicious campaign has also affected telecommunications infrastructure in other countries, highlighting the global nature of cybersecurity threats.

Deloitte UK Reportedly Cyberattacked for 1 TB of Sensitive Data by Ransomware Group

Deloitte UK Reportedly Cyberattacked for 1 TB of Sensitive Data by Ransomware Group

The Brain Cipher Ransomware group has reportedly claimed responsibility for a significant cyberattack on Deloitte UK, alleging that they have exfiltrated over 1 terabyte of data. This breach, if confirmed, could have serious implications for Deloitte's clients and its professional reputation.

However, Deloitte has not confirmed the breach, leaving the claim unverified.

The group claims to have accessed and stolen over 1 terabyte of compressed data, including sensitive client information and internal documents.

According to statements posted by Brain Cipher, the attack has exposed critical vulnerabilities in Deloitte UK’s cybersecurity infrastructure. “Soon we will tell you about this incident. We will provide an example of data that has leaked. The volume of compressed data more than 1tb".

The group has criticized Deloitte for not observing basic information security protocols. "Unfortunately, giant companies do not always do their job well,” the hackers claim.

Brain Cipher emerged in June 2024 and has quickly gained notoriety for targeting high-profile organizations.

Brain Cipher has set a deadline of December 15, 2024, for Deloitte to respond, after which they threaten to release the stolen data.

The impact of this breach could be severe when it comes to client data exposure. Potential exposure of sensitive client information, including financial records, could be affected. Reputational Damage of the "big four" firm is also at stake. As one of the world's leading professional services firms, Deloitte's stature is at stake as it is raising serious concerns about data protection practices.

The breach, if confirmed, could disrupt operations for Deloitte and its clients, eroding trust and confidence.

Deloitte has yet to confirm the incident publicly. This situation underscores the critical need for robust cybersecurity measures in today's digital landscape.

Cisco Firewalls Infiltrated by State-Sponsored Spies To Access Govt Networks

Cisco Firewalls Infiltrated by State-Sponsored Spies To Access Govt Networks

There has been a significant cybersecurity incident involving Cisco firewalls. A campaign known as ArcaneDoor has been identified as the latest example of state-sponsored actors targeting perimeter network devices, including those from Cisco. This sophisticated campaign has been found to compromise multiple government networks globally.

On Wednesday, Cisco warned that its so-called Adaptive Security Appliances —devices that integrate a firewall and VPN with other security features — had been targeted by state-sponsored spies who exploited two zero-day vulnerabilities in the networking giant's gear to compromise government targets globally in a hacking campaign it's calling ArcaneDoor.

There is a risk of sensitive data being compromised, which can include classified government information, intellectual property, and personal data of citizens and employees. The affected countries have not been specifically listed by Cisco, but given the global use of Cisco's network devices, it's likely that multiple countries across different regions have been impacted. Organizations using Cisco Adaptive Security Appliances (ASA) devices and Cisco Firepower Threat Defense (FTD) are strongly encouraged to apply the necessary updates and monitor their systems for any signs of compromise. 

Cisco Talos, the company's intelligence and interdiction team, has been working with external intelligence partners to investigate the matter. They have discovered two backdoors, named "Line Runner" and "Line Dancer," used by the attackers to conduct espionage activities. These activities include configuration modification, reconnaissance, network traffic capture/exfiltration, and potentially lateral movement within the networks.

The attackers, tracked as UAT4356 by Talos and STORM-1849 by the Microsoft Threat Intelligence Center, have shown a clear focus on espionage and an in-depth knowledge of the devices they targeted. Cisco has also identified two vulnerabilities, CVE-2024-20353 and CVE-2024-20359, and is advising customers to follow the guidance published in the security advisories to protect against these threats.

Cisco has released security updates to fix the vulnerabilities and is strongly recommending customers to upgrade their devices to prevent further attacks. It's a reminder of the importance of network security and the need for vigilance in monitoring and updating network devices to prevent such intrusions.

The implications of the Cisco firewall breach are significant and multifaceted. The breach has exposed vulnerabilities in network devices that are critical for the security of government and corporate networks. The exploited zero-day vulnerabilities allowed attackers to gain unauthorized access and potentially take full control of the compromised devices.
 
Cisco Firewalls Infiltrated by State-Sponsored Spies To Access Govt Networks

The nature of the attack suggests that it was carried out for espionage purposes, which means that state secre6ts, strategic plans, and other sensitive information could have been targeted for intelligence gathering.

Targets

The ArcaneDoor campaign has been reported to target government networks worldwide, exploiting vulnerabilities in network devices to breach these systems. While specific countries have not been listed in the available reports, it's mentioned that telecommunications providers and energy sector organizations have seen a dramatic and sustained increase in targeting, which suggests that critical infrastructure entities in various countries are likely strategic targets of interest for the state-sponsored actors behind ArcaneDoor.

Given the global nature of the targeted devices and the sophistication of the attacks, it's reasonable to infer that multiple countries across different regions might be affected. The campaign's focus on espionage and the use of advanced persistent threats (APTs) indicate a broad and potentially global scope of operations. Organizations worldwide, especially those in critical infrastructure sectors, should be vigilant and proactive in securing their network devices against such threats.

Such breaches can erode confidence in an organization’s brand and the security of its products. This can have long-term effects on customer trust and business relationships.

The breach can result in lost productivity and potentially cost millions of dollars in damages, both in terms of immediate incident response and long-term remediation efforts. This attack can knock network systems out of commission, disrupting the normal operations of government agencies and businesses.

Organizations are encouraged to monitor system logs for signs of compromise, such as unscheduled reboots, unauthorized configuration changes, or suspicious credential activity.

Overall, the breach underscores the importance of robust cybersecurity measures, including regular updates, monitoring, and the use of strong multi-factor authentication to protect against such sophisticated threats. It also highlights the ongoing challenges of securing network perimeters against state-sponsored cyber activities.

With 13.7% of All Cyber Attacks, India is Most Targeted Country; 100% Increase in State-Sponsored Attacks

With 13.7% of All Cyber Attacks, India is Most Targeted Country;  100% Increase in State-Sponsored Attacks
  • India is the most targeted country with 13.7% of all cyber attacks directed at it
  • US, Indonesia and China are next 3 most targeted countries by threat actors
  • Govt agencies across nations emerge as the topmost target with 95% of the cyber attacks aimed at them
  • State sponsored cyber attacks increased by 100% on India in 2022
  • Healthcare sector most targeted in India followed by education, research, govt and military sectors
  • Cyfirma research shows 39 active campaigns against India in 2023 coming from state sponsored threat actors from China, North Korea, Pakistan, Russia
  • Threat actors actively targeting India include FancyBear, Mission 2025 (China), TA505 (Russia), Transparent Tribe (Pakistan) Turla Group, Stone Panda and Lazarus Group (North Korea)
CYFIRMA, an external threat landscape management platform, has released India Threat Landscape report 2023 focusing on threats targeting India and strategies to counter them.

According to the report, India is the most targeted country, with 13.7% of all attacks followed by the US with 9.6%, Indonesia and China with 9.3% and 4.5% respectively. The number of cyberattacks on government agencies has increased significantly year-on-year. In the second half of 2022, there were 95% more cyberattacks on government agencies than in the same period in 2021. The number of state-sponsored cyber attacks in India increased by more than 100% in 2022 compared to 2021. India was the most targeted country in 2022 as attacks on government agencies more than doubled.
 
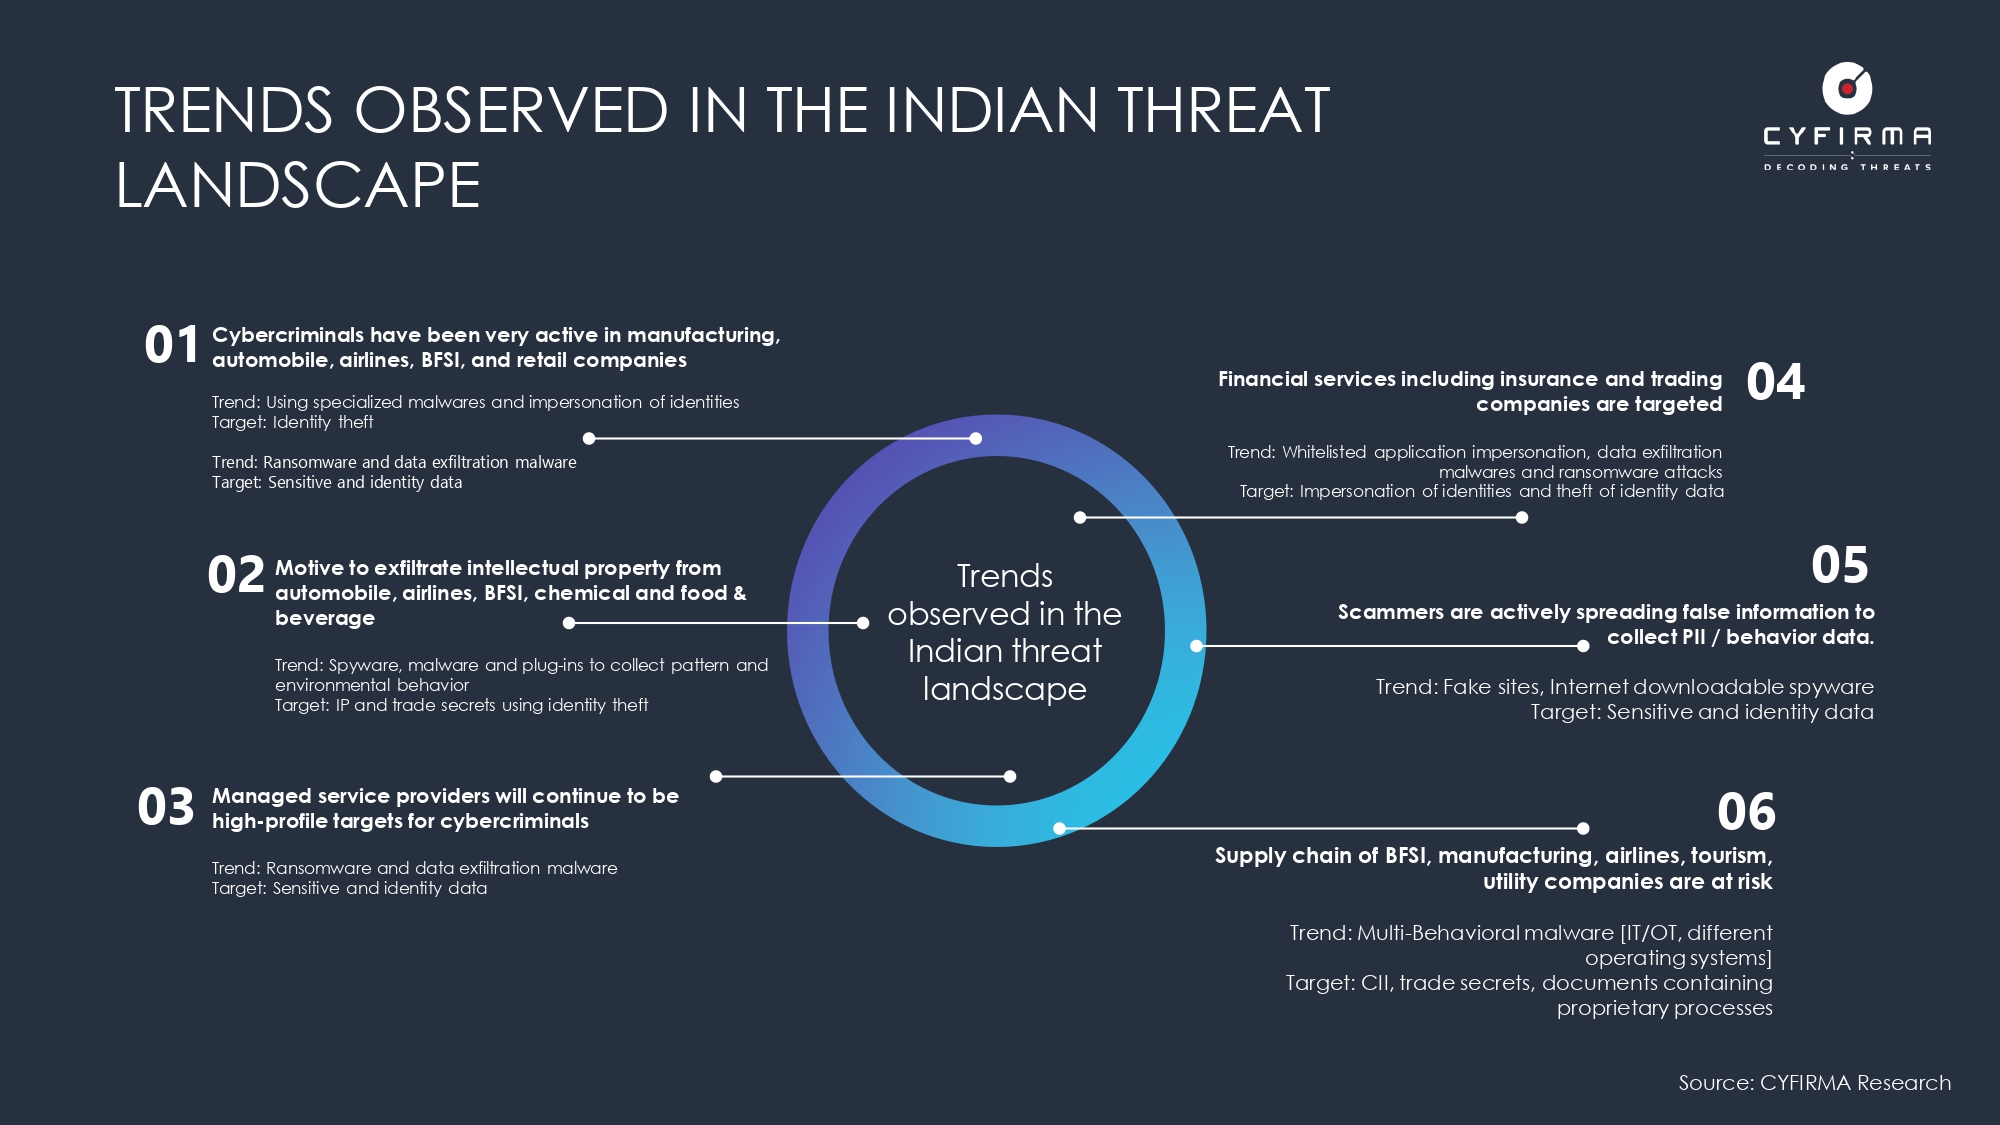
TRENDS OBSERVED IN THE INDIAN THREAT LANDSCAPE

Healthcare is the most targeted sector by hackers followed by education, research, government and military sectors. The data from the report shows that an organization in India was attacked 1,866 times per week on average in 2022.

The most common types of cyber attacks in India are — phishing attacks, malware attacks, and ransomware attacks. 78% of Indian organizations experienced a ransomware attack in 2021, with 80% of those attacks resulting in data encryption.

 
INDIAN THREAT LANDSCAPE PHISHING

BILLIONS SPENT - YET UNABLE TO PROVIDE THE RIGHT LEVEL OF PROTECTION

Kumar Ritesh, CEO & Founder, Cyfirma, says, “It comes as no surprise that India is the most targeted country in the world by threat actors. India’s growing prominence at the world stage and push from Western economies to favour India over other large countries, a young and tech savvy population with low cybersec maturity has played a key role in hackers coming after critical assets, govt agencies with an intent to breach them and harm India’s strategic interests. While sectors like BFSI, healthcare and software companies have spent significantly on improving their security posture, there is an urgent need to understand the external threat landscape. We believe that unless you don't know who to defend against, billions spent in cybersec will not yield expected results.”

India’s geo-political importance has never been greater than it is today. This has given way to threat actors uniting against India. A disturbing trend of North Korean threat actors collaborating with China and Russia has been observed with the former offering itself as hacker as a service (HaaS) for financial gains.

Between Jan to July 2023, as part of the external threat landscape monitoring and analysis, CYFIRMA observed 39 campaigns targeting various industries in India. Known groups like FancyBear, TA505, Mission 2025, Stone Panda and Lazarus Group are suspected to be behind these campaigns. Of these 39 campaigns, 14 have been orchestrated by China State sponsored groups with an intent of espionage. 11 of these campaigns were planned by North Korea backed hackers as part of HaaS. While 10 attacks originated from Russian threat actors, of which only 4 were state sponsored.

Key trends and attack methods being used by threat actors:

Ransomware: Ransomware operators are continuously improving their techniques with an intent to intimidate and force victims to pay the ransom. At present, ransomware operators are suspected to follow a 4-layer approach of targeting organizations which includes:
  1. Infiltrate into the target organization’s network.
  2. Exfiltrate and encrypt data.
  3. Demand ransom and “Name & Shame”.
  4. Leave behind footprints in the targeted organizations to come back and attack again.
Crimeware- as-a service: CaaS threats include SMS spoofing, phishing kit,custom spyware, hackers for hire, exploit kit.

Carpet Bombing of SMEs: SMEs are not spared by cyberwar, businesses of all sizes are targeted.

Supply Chain disruption: Software supply chain will continue to be targeted

With the rising attacks, it is critical for the govts and Organizations to engage a comprehensive ETLM tool, which can take the intel gathered and relate it back to infrastructure, digital footprint, brand, industry, technology, and geolocation. Because when you unify different capabilities, you get a prioritized list of actions to prepare an effective response plan.

CYFIRMA is an external threat landscape management platform company. We combine cyber intelligence with attack surface discovery and digital risk protection to deliver early warning, personalized, contextual, outside-in, and multi-layered insights. Our cloud-based AI and ML-powered analytics platforms provide the hacker’s view with deep insights into the external cyber landscape, helping clients prepare for impending attacks. CYFIRMA is headquartered in Singapore with offices in Japan, India, the US, and the EU. Customers include both government as well as Fortune 500 companies across manufacturing, financial services, retail, industrial products, natural resources and pharmaceutical Industries.


Ethereum Inventor Vitalik Buterin’s X (Twitter) Account Hacked Leading $691K+ Losses from Victims' Accounts

Ethereum Inventor Vitalik Buterin’s X (Twitter) Account Hacked Resulting $691K+ Loss from Victims' Accounts

Vitalik Buterin, Ethereum’s inventor & co-founder, reportedly had his X (formerly Twitter) account hacked, resulting into loss of $691,000 from users who followed a malicious link posted to his X feed.

According to prominent blockchain investigator ZachXBT, the hacking incident has led to victims collectively losing over $691,000 after clicking on a corrupted link.

Dmitry Buterin, the father of Vitalik, announced on Sep. 9 in a post at X that his son’s account had been compromised and Vitalik is working on restoring access.

The account hack was first noticed on Saturday when a post appeared on Buterin’s post announcing the launch of a set of commemorative non-fungible tokens (NFTs) from software provider Consensys.

This post has a malicious link, which could have been displayed to a large number of Vitalik's 4.9 million followers, and prompted followers to follow the link and eventually connect their wallets to mint the NFT, but in reality, it allowed the hacker(s) to get access to their funds in their wallets.

The post on Vitalik's account was later deleted. However, the damage was done already.

This incident has even led Ethereum developer Bok Khoo, better known as Bokky Poobah on X, to allegedly suffered losses in his CryptoPunk NFT collection.

Notably, no official comment has been made by Vitalik, so far, in this hacking incident. According to ZachZPT, the hacker subsequently sent a stolen NFT to Vitalik.


Apply Ancient Wisdom To Your Digital Lives: Cyber Security DCPs

Apply Ancient Wisdom To Your Digital Lives: Cyber Security DCPs
  • Most of the victims of cyber fraud or crime, 95% of them are well-educated and 80% are software professionals: Cyber Crime DCPs
  • Cyber Crimes are becoming more organised now: Ms Ritraj, DCP, Cybercrimes, Cyberabad
  • If you are using ChatGPT, even cybercriminals are also using it. Be alert, tell experts
  • Report Cyber Crimes to the 1930 helpline
FLO (FICCI Ladies Organisation) organised a session “Unlocking Cyber Secrets’, on Safe Guarding Against Digital Threats with three top cyber expert police officers of Telangana Police at Integrated Control and Command Center at Jubilee Hills on Friday. 

The session was inaugurated by Mr CV Anand, Police Commissioner, Hyderabad.

Giving her opening remarks, Ritu Shah, Chairperson of FLO said, Cybersecurity is a social responsibility. We all have a role to play, she said quoting Magda Chelly, a noted expert on Cyber security.

We are living in an age where technology seamlessly intertwines with every facet of our lives. From the moment we wake up to the time we rest our heads on our pillows, technology accompanies us like a steadfast companion. Cybersecurity is the bedrock upon which our digital society rests, ensuring the integrity, confidentiality, and availability of data and systems that shape our modern existence. It's a profound honour to welcome you to this distinguished panel discussion, "Unlocking Cyber Secrets, Safeguarding Against Digital Threats”, she said.

This discussion promises to unveil insights, strategies, and solutions to protect our digital landscape, she added.

Participating in the panel discussion moderated by Mr Santosh Kaveti, CEO and Founder of ProArch, Ms Sneha Mehra, IPS, DCP Cyber Crimes, Hyderabad; Dr B. Anuradha, DCP Cyber Crimes, Rachakonda, and Ms Ritraj, DCP Cyber Crimes, Cyberabad, said people must be able to differentiate who is a foe and who is a friend. Most of the victims of Cyber Fraud, it is very sad to note that are well-educated. 95 per cent of them are highly qualified. And 80 per cent of them are Software professionals.

Apply Ancient Wisdom To Your Digital Lives: Cyber Security DCPs
(Right-most) CV Anand - Police Commissioner Of Hyderabad Seen inaugurating Session on Cyber Security also seen are Ritu Shah, Sneha Mehra, Dr Anuradha

Cybercrimes are happening because of a lack of logical thinking, and awareness. People must use common sense, they added. 

Another reason for becoming a victim of many cyber frauds is a lack of Cyber Hygiene. The practices and steps that users of computers and other devices need to take regular initiatives to maintain system health and improve online security. These practices, said Ms Sneha, are often part of a routine to ensure the safety of identity and other details that could be stolen or corrupted.

Apply Ancient Wisdom To Your Digital l Lives: Cyber Security DCPs
(L-R) Ritu Shah , Sneha Mehra, Dr B Anuradha and Ritraj DCPS

Safe Cyber Transactions must become part of your daily conversations, advised Ms Sneha Mehra.

Cyber Criminals use public fear, greed, and guilt as their opportunities and their weapons to cheat people. You must be aware of this fact. If somebody promises easy money, the simple thing is to use your common sense. Illiterate people are safe because they use common sense. But unfortunately, many learned people who are falling prey to these cyber crooks are not using their minds. Think before you act, Dr Anuradha said.

She narrated how a woman who returned from abroad recently fell prey to a part-time job racket and lost rupees two crores a couple of days back in Rachakonda, is now living in guilt for ignorantly sharing a ten-second nude video to come out of the mess she landed in. She is now being counselled by a professional appointed by Rachakonda Police. 

When she approached the police along with her husband, it was too late and scamsters syphoned of the booty through 100 different accounts and the money had gone down through 30 layers and the police were helpless, Dr Anuradha added. 

Another sad thing is despite being social animals, many people in these kinds of situations suffer in silence and don’t share with any of their family members and friends. 

Santosh, the moderator reminded 150 plus FLO members of the Thirty Crow story and advised them not to be greedy and get tempted by easy money offers. They must cross-check, verify and consult experts before they act upon them. If the crow could use its common sense so as we, he said.

Another fraud that is trending off-late is that cybercriminals are taking the help of ChatGPT to draft alluring and tempting messages, offers that you are bound to take seriously. So be aware of these trends and act accordingly, he said. 

Ritraj said cyber crimes are becoming more organised. They are trying to get more professionals.

Referring to many calls people receive in the disguise of SBI Bank, she said, no public sector bank like SBI calls you at odd hours or after bank hours. They don’t call you from a private number. They don’t use social media to communicate. She advised people to think logically and act, she said.

You can report it to the 1930 helpline or log in National Cyber Crime Reporting Portal and report it they advised the public.

Juice Jacking: A New Cyber Stealing that Empties Bank Account When Smartphones Connect To Charging, RBI Warns

Juice Jacking: A New Cyber Stealing that Empties Bank Account When Smartphones Connect To Charging, RBI Warns

You may have hardly noticed this, but today big-fatvhackers around the world are stealing people's confidential data by planting 'malware' in public cables or USB ports. This is called 'Juice Jacking'.

Cyber ​​thieves are adopting new tactics every day. Some are cheating people by sending messages on WhatsApp, while some are cheating by sending YouTube video links to like. Juice Jacking is also a type of scam about which very few people know. Many of you may already know about it and many may not know, but this juice jacking can destroy your entire life's earnings in a jiffy. India's central bank, Reserve Bank of India (RBI) has issued a warning regarding this.

Let us know what is juice jacking and what is the way to avoid it?

Juice jacking is a type of cyber stealing, where, once your mobile is connected to unknown / unverified charging ports, unknown apps / malware are installed with which, the fraudsters can control / access / steal sensitive data, email, SMS, saved passwords.

Precaution —

Always avoid using public/ unknown charging ports/cables.

When battery of your mobile, tablet or laptop runout at times when you're at public place like a railway station, airport or hotel, and you may start charging the device with the charging cable or USB port you see there, but have you thought that the battery of the device gets charged? Your bank account could be empty or your private messages, emails, mobile passwords or other information could be stolen.

Steps To Follow To Avoid Juice Jacking
  • Never use the pre-installed charging cable in train, airplane or at station-hotels.
  • Don't use the charging cable or port that you get as a promotional gift.
  • Use the original charger and cable that came with your phone.
  • If you are traveling then keep a power bank with you.
  • Use an adapter instead of using the USB port at a charging station.
  • Do not charge phone or any other Gadgets using USB port at hotels. 

Cyber Attack on Madhya Pradesh Power Management Co.'s Servers

Cyber Attack on Madhya Pradesh Power Management Co.'s Servers

The power management company in Jabalpur, Madhya Pradesh has been stalled for the last several days. The IT cell of the power management company has filed a complaint in Gorakhpur police station of Jabalpur, considering this problem as a cyber attack.

Cyber attack occurred on the server of MP Power Management Company, which caused the internet to go down in the company's office that made PMC unable to function. The company's account is also threatened. Apart from this, information about buying and selling electricity is also expected to be leaked.

For last 4 days, the company's IT cell has been involved in locating the cyber attack, but has no any firm information on its hand.

Ironically, in September last year Madhya Pradesh become the first state of the country to implement cyber crisis management plan developed by M.P. state load dispatch centre Jabalpur. Notably, Cyber Crisis Management Plan was developed in-house without taking the help of expert consultants and implemented after approval by Computer Emergency Response Team (CERT-India), a government organization that responds to computer security incidents and promotes IT security practices and functions under the Ministry of Electronics & Information Technology

MP Power Management Company is the most important company in Madhya Pradesh's power system, and it takes care of when, where and how much electricity the state needs and where it will be completed.

With electricity, there is a big drawback that it cannot be stored, so electricity has to be supplied at the same time when it is produced. The information on the availability of electricity at different power generation plants across the country are being tracked on the computers of the power management companies, through the Internet. The power management company buys electricity from companies with which it has power agreements.

Earlier officials of the power management company did the investigation, but the internet system was not able to improve. It was then understood that this is not a general technical flaw, but something else has damaged the MP Power Management Company's system. Although no virus or message like previous cyber attacks is displayed to the computer of a power management company, it has been considered a cyber attack.

Madhya Pradesh has a capacity to generate about 6000 MW of electricity and many a times some electricity remain unused by the state so it is then sold to other states. This entire process of buying & selling electricity is done on computer through internet and this buy-sale transactions are worth billions of rupees, But the computer system that has been installed for such an important and extremely important business.

Reportedly, the MP power management company did not take care of security of computer systems and using cyber security solutions like domestic computers. When when the internet stopped providing services, the PMC authorities did not consider it a cyber-attack. The PMC personnels however are not at fault because they are not trained enough in the field of Cybersecurity.

According to an PMC official, the company's servers are unable to do any work due to disturbances. All work from human resources is being affected. Only the IT department can provide information about technical malfunction in the server.


Cyberabad Police Cracked India's Biggest Ever Data Theft: Data of 66.9 Cr Individuals and Organisations Across 24 States, 8 Metros Stolen

India's biggest ever data theft: Personal and confidential information of 66.9 cr individuals and organisations, across 24 states and 8 metros stolen and 1 arrested

The accused allegedly possessed 18 lakh students' records from Byju's and Vedantu, 1.84 lakh records for cab users, and 4.5 lakh records for salaried worker. 

Data is new age currency and some fraudsters derived plans to make quick bucks by selling the sensitive data. Cyberabad Police cracked yet another biggest-ever data theft case in the country. This time it is much bigger than what was cracked a few days ago. This time Personal and confidential information of 66.9 cr individuals and organisations across 24 states and metro cities was stolen.

The accused identified as Vinay Bhardwaj arrested. He established an office in Faridabad, Haryana and collected databases from Amer Sohail and Madan Gopal. He used to promote social media platforms to resell the data to fraudsters for profits.

According to CyberabadPolice, the accused was found possessing data of students of Byjus & Vedantu organisations. Also, he possessed the data of 1.84 lakh cab users of eight metro cities and data of 4.5 lakh salaried employees of six cities and Gujarat state. Further, the accused holds consumer/customer data of major organisations like GST (Pan India), RTO (Pan India), Amazon, Netflix, Youtube, Paytm, Phonepe, Big Basket, BookMyShow, Instagram, Zomato, Policy Bazar, Upstox, etc


The accused person is found selling personal and confidential data of about 66.9 crore individuals and organisations maintained in 104 categories. This includes 51.9 crores of data of individuals and organisations of 24 states and 8 cities maintained in 44 categories.

According to the Police, some of the important data held by the accused include the data of defence personnel; government employees; PAN card holders; students data of 9th, 10th, 11 & 12th standard; senior citizens; Delhi electricity consumers; D-MAT account holders; mobile numbers of various individuals; NEET students; High Net worth Individuals; insurance holders; credit card and debit card holders etc

In this case, the accused person was operating through a website “InspireWebz” in Faridabad, Haryana and selling databases to the clients through cloud drive link
The accused is holding data of 4.5 Lakh salaried employees of six metropolitan cities and Gujarat state.

Some of the important categories are data of Banks, Insurance & Financial Services, Doctors, Software Engineers, True-caller & Telecom Data, Trading & Stockbroking, Consulting services of crores of individuals etc including the personal and confidential data of Defence, Government employees, PAN card holders, High Networth Individuals, D-MAT account holders, students database, Financial data(Credit card, Debit Card, Loans and Insurance) was found available with these accused.
Data of NEET students with their names, father name, mobile number & their residences are also found with these accused. PAN Card database containing sensitive information on income, email ids, phone numbers, addresses etc was also found. Data of Government employees containing information on their name, mobile number, category, date of birth etc was also found.

Further, the database of the car owners of vehicles, Job Aspirants data, Real Estate, Construction, Manufacturing & Industrial, Frequent Flyer Travel details, NRI Database, etc was also identified with them.

The Police have seized from his possession two mobile phones, two laptops and Data of 135 categories containing sensitive information of government, private organisations and individuals

Categories of Data Found With Accused Persons


State/ City Wise

Total Count

1.WEST BENGAL

70 Lakh

2.UTTAR PRADESH

21.39 Crore

3.TAMILNADU

1.02 Crore

4.RAJASTHAN

2 Crore

5.PUNJAB

1.5 Crore

6.PUNE

12 Lakh

7.ODISSA

30 Lakh

8.NORTH EAST

60 Lakh

9.MUMBAI

46 Lakh

10MAHARASHTRA

4.50 Crore

11.MADHYA PRADESH

1.10 Crore

12.KOLKATTA

46 Lakh

13.KERALA

1.57 Crore

14.KARNATAKA

2 Crore

15.JAMMU & KASHMIR

25 Lakh

16.JAIPUR

68 Lakh

17.HYDERABAD

56 Lakh

18.HARYANA

1 Crore

19.DELHI NCR

20 Lakh

20.DELHI

2.70 Crore

21.CHENNAI

70 Lakh

22.BIHAR

1 Crore

23.BANGLORE

60 Lakh

24.ASSAM

90 Lakh

25.ANDHRA PRADESH

2.10 Crore

Total

48.4 CR

Category Wise

Total Count

26. Job Seekers Database 

40 lakhs

27. Domain Whois Database

3.47 crore

28. Schools, Colleges, Universities & Education 50000

4.2 lakhs

29. Teachers Database

5.7 lakhs

30. Advocates & Lawyers

1.64 lakhs

31. Agents

28000

32. Apparel & Garments

65200

33. Architect & Interior Designers 

65000

34. Beauty Parlors, Hair Cutting Saloons & SPA 

70000

35. BPO Call Center Employees

2.6 lakhs

36. Building Material & Requisites

15500

37. Business Analyst 

25000

38. Business Development & Sales Professionals 

1.5 lakhs

39. Cab Users

1.84 lakhs

40. CBSE School Email IDs

18000

41. Cell Phones & Accessories Shops

13600

42. CEO, CFO, CTO, CMO 

2 lakhs

43. Channel Sales Persons Database

50000

44. Chartered Account 

42000

45. Chemical Pharma Companies Database

39000

46. Chemists Dtababase

1.23 lakhs

47. Chief Managers

20800

48. Civil Engineer 

2.53 lakhs

49. Club Mahindra 

3.26 lakhs

50. Commercial & Residential Properties

29000

51. Company MD, Secretatiaty & Chairmen Database

5.2 lakhs

52. Company Proprietors Database

3.9 lakhs

53. Computer Laptop Dealers Database

17000

54. Computer, IT & Telecom Services

54000

55. Consultants & Consulting Services Database

2.04 lakhs

56. Contractors Database

10900

57. Credit Card Holders 3000000

98 lakhs

58. CRM, Call Centres BPO Executives Database

1.2 lakhs

59. Dealers Database

20000

60. Debit Card Holders

8.1 lakhs

61. Defence Force Delhi NCR Database

2.55 lakhs

62. Designers Database

50000

63. Digital Photography Studios Database

58000

64. Dining Leisure Customers Database

24000

65. D-Mat Account Holders

35 lakhs

66. DTP Operators Database

14000

67. Economic Analysts Database

13500

68. Educational Institutes Database

11100

69. Electricals Electronics Stores Database

1.5 lakhs

70. Employees Delhi NCR Bank Database

34000

71. Energy Power Sector Delhi NCR Database

23600

72. Female Consumer Bangalore Database

1.17 lakhs

73. Financial Analysts Managers Industry Database

1.04 lakhs

74. Food Beverage Stores Database

31000

75. Freelancers 76000

76000

76. Frequent Flyer 1.60 Lac

18 lakhs

77. Furniture Furnishing Business Database

27000

78. Gas Petroleum Database

1.03 lakhs

79. Gems Jewellery Shops Database

34000

80. General Managers Database

14.6 lakhs

81. Government Employes 110000

11 lakhs

82. Graphic Designers Database

48000

83. Gymnasiums 24000

24000

84. Health Beauty Shops Business Database (1)

54000

85. HNI & High Income Employee 5 Lac

5 lakhs

86. Home, Garden Pets Suppliers Database

29000

87. Hotels, Restuarants, Restro Bars, Outlet 2 Lac

2 lakhs

88. HR - Human Resources Database

38500

89. Importers Database

1.06 lakhs

90. IT Companies Database

39000

91. IT Professionals, Hardware Networking Working Employees Database

15 lakhs

92. Jewellers Database

14800

93. Lecturer Professor Database

25000

94. Legal Firms Database

11455

95. LIC Agents Emails Database

10962

96. Logistics Management Service Providers Database

87653

97. Industrial Equipments Machinery Suppliers Database

52000

98. Male Gents Database

22 lakhs

99. Manufacturing Companies Database

1.6 lakhs

100. Metals Minerals Industries Database

15850

101.MLM Leader Emails Database

1.12 lakhs

102. Mobile Number Database

3 crores

103.NGO Trusts Database

22034

104.NRI (non Resident Indians) 126633

1.26 lakhs

105.OLX 1500000

15 lakhs

106 Pancard Holder 1500000

15 lakhs

107. Photographers Database

28000

108. Placement Agencies Database

48300

109. Policy Bazaar Database

7.8 lakhs

110. Principals Database

14180

111. Printing Packaging Companies Database

43408

112. Project Leader Managers Database

32000

113. Purchase Procurement Heads Database

47125

114. Purchase Managers Database

67638

115. Real Esate Industry Database

4 lakhs

116. Recruitment Agencies Database

49900

117. Religares Database

4.13 lakhs

118. Retail Shops 35000

35000

119. Samaj Community Wise 2 Crore

2 crores

120. Semi Government Industries Database

19340

121. Senior Citizens 2000000

10.6 lakhs

122. Services Industries Database

1.88 lakhs

123. Shopping Malls, Firms Shops Database

81441

124. Software Engineers Database

2.7 lakhs

125. Steel Steel Products Industries Database

1.17 lakhs

126. Stock Broking Trading Companies Database

2.06 lakhs

127. Stock Traders 700000

7 lakhs

128.CBSE Students data (10th & 12th Class)

30 Lakh

129.BYJUS & VEDANTU database

18 lakhs

130. STUDENTS Database

2 crores

131.NEET STUDENTS Database

1.8 lakhs

132.9th & 10th STUDENTS Database

1.5 crores

133. NRI Database

1.2 lakhs

134.Facebook And Instagram Groups Database

800

Total 

64 crores


Data Categories & Information


State/City wise:

  1. Andhra Pradesh

  2. Bihar

  3. Haryana

  4. Himachal Pradesh

  5. Delhi

  6. Karnataka

  7. Maharashtra 

  8. Kerala

  9. Madhya Pradesh

  10. Odisha

  11. Punjab

  12. Rajasthan

  13. Uttar Pradesh

  14. Meghalaya 

  15. Nagaland

  16. Arunachal Pradesh

  17. Assam

  18. Jammu & Kashmir

  19. Jharkhand

  20. Tripura

  21. Telangana

  22. Tamil Nadu

  23. West Bengal

  24. Gujarat


Category Wise:

1.    Advertising, PR & Events

2.    Apparel Garments, Gems & Jewellery

3.    Automobiles

4.    Banks, Insurance & Financial Services

5.    BPO, CRM & Call Centres 

6.    Broker, Trading & Stockbroking

7.    Business Development & Sales Professionals

8.    CA, Chartered Accountant

9.    Client Servicing, Event Management & Road Show Advertising

10.    Company Secretary, Accounting, Tax & Audit

11.    Construction, Cement, Metal & Steel Iron

12.    Consultants

13.    Consulting Services, Recruitment & Placement Agencies

14.    Doctors, Nurses & Medical-

15.    Educational & Training

16.    Electrical & Electronic-

17.    Engineer

18.    Entertainment & Media

19.    Event Management

20.    Export & Import

21.    Freelancers

22.    Hotel, Restaurant & Food Services

23.    HR Managers, Human Resources, HR Heads & Professional

24.    IT Hardware & Networking

25.    IT Softwares

26.    Lawyers, Legal Law & Legal Firms

27.    Lecturer & Professor

28.    Logistics, Freight Forward & Courier Distribution

29.    Media Planning

30.    Medical Representative

31.    NGO & Social Services

32.    Printing & Packaging

33.    Project Leader & Project Manager

34.    Real Estate

35.    Sales Marketing & Marketing Head

36.    Software Engineers

37.    Teaching & Education

38.    Ticketing, Reservation, Travel Agent & Airlines

39.    Top Management

40.    Travel, Tourism, Airlines & Hospitality

41.    Only Mobile Numbers

42.    Mobile Numbers with Name data

43.    Mail ID's Data

44.    Truecaller & Telecom Data


Assam

Total Count: 90Lakh

Category Wise Data Base:

  1. Mobile no’s data with address

  1. Mobile no’s data

Fields:

  1. Name

  1. Mobile No

  1. Pincode

  1. Cirty


Jammu & Kashmir

Total Count: 25 Lakh

Category Wise Data Base: 

  1. Mobile No’s Data

Fields:

  1. Name

  1. Email ID

  1. Mobile

  1. Category

  1. City

  1. Address


Tamil Nadu

Total Count: 1.02 crore 

Category Wise Data Base:

  1. City wise Mobile Data

  1. Mobile no’s data

Fields:

  1. Name

  1. Mobile No

  1. Pincode

  1. Cirty

  1. Address


Arunchal Pradesh, Assam, Meghalaya, Nagaland & Tripura (N.E)

Total Count: 60 Lakh 

Category Wise Data Base:

  1. City wise Mobile Data

  1. Mobile no’s data

Fields:

  1. Name

  1. Mobile No

  1. Pincode

  1. Cirty

  1. Address


Bangalore

Total Count: 60 Lakh

Category Wise Data Base:

  1. Email ID

  1. Mobile No’s Data

Fields:

  1. Name

  1. Mobile No

  1. City

  1. Pincode

  1. Address


Hyderabad

Total Count: 56 Lakh

Category Wise Data Base: 

  1. Salaried Data base (Accounting/Tax/Company Secretary/Audit)

  1. Mobile no’s Data

Fields:

  1. Name 

  1. Email id

  1. Mobile no

  1. Industry/ occupation

  1. City

  1. Address


Chennai

Total Count: 70 Lakh

Category Wise Data Base: 

  1. Mobile no’s Data


Fields:


Badges

Score

SpamCount


  1. Number

  1. Carrier

  1. Name

  1. Gender

  1. Address

  1. JobTitle

  1. CompanyName

  1. Email

  1. Website

  1. Facebook

  1. Twitter

  1. Tags

  1. Badges

  1. Score


Mumbai

Total Count: 46 Lakh 

Category Wise Data Base:

  1. Mobile no’s data with address

  1. Mobile no’s data

Fields:

  1. Name

  1. Mobile No

  1. Pincode

  1. Cirty

  1. Address


Pune

Total Count: 12 Lakh 

Category Wise Data Base:

1.Mobile no’s data with address

Fields:

  1. Name

  1. Mobile No

  1. Pincode

  1. Cirty

  1. Address


JAIPUR

Total Count: 68 Lakh 

Category Wise Data Base:

Students Categories

  1. 12 th Pass out 2014

  1. Rajasthan 12 th pass out 2015

Fields:

  1. Student Name

  1. fname

  1. mname

  1. dob

  1. medium

  1. gender

  1. cat

  1. board

  1. occupancy

  1. add1

  1. add2

  1. add3

  1. city

  1. district

  1. pincode

  1. state

  1. study

  1. phone1

  1. phone2

  1. mobile1

  1. mobile2

  1. email

  1. mobile


Whats app no’s Categories

  1. Caterers

  1. Courier

  1. Engineers

  1. Gas agency

  1. Hotels

  1. Logistics

  1. Resort

  1. Sweet

  1. Tea

  1. Tours

  1. Transports

  1. Travel

  1. Water


Fields:

  1. Mobile

  1. Company


Categories:

  1. Card holder data

  1. Computer Dealers

  1. Courier customer list

  1. Eyes Doctors

  1. Hotels

  1. Interior Design and Architecture

  1. Auto Mobile Directory

  1. Car Owners

  1. Doctors

  1. E-Commerce

  1. Females

  1. India Mart Data Base

  1. Jewelleries

  1. Job seeker Data

  1. Real Estate Data

  1. Travel agencies

  1. VID Card Data

  1. Just Dial and OLX Data

  1. Bank Users Jaipur

  1. Clubs Data

  1. Golf club Directory

  1. Club of permanent members

  1. Club of Quasi members

  1. Club of temporary members

  1. Social Groups

  1. Tower Data

  1. Ladies Club

  1. Mobile Numbers Data


Fields:

  1. Name

  1. mobile no

  1. Address

  1. City

  1. Email


Job seekers data fields:

  1. Area of Specialization

  1. Industry

  1. Resume Title

  1. Key Skills

  1. Current Salary

  1. Level

  1. City

  1. Preferred Location

  1. Course (Highest Education)

  1. Specialization (Highest Education)

  1. Institute (Highest Education)

  1. Course (2nd Highest Education)

  1. Specialization (2nd Highest Education)

  1. Institute (2nd Highest Education)

  1. Gender

  1. Address

  1. Resume Id


Paytm 

Total Count: 50 Lakhs

Fields:

  1. S.No

  1. Paytm Customer Name

  1. Customer Mobile

  1. Customer_Email

  1. Gender

  1. Bank

  1. City

  1. State

  1. Income declared

  1. Proof

  1. Type of acTotal Count


Phonepe Data Base 

Total Count: 1.8 Lakh

Fields:

  1. Customer Name

  1. Bank

  1. Person_EmailId

  1. Phone Pay Number

  1. Address

  1. City


YouTube database

Total data: 62.3 Lakhs

Fields:

  1. S.No

  1. Channel Name

  1. Address

  1. City

  1. MOBILE

  1. Email id 

  1. CATAGERY


Net Flix 

Total data: 22 Lakhs

Fields:

  1. NETFLIX USER NAME

  1. AREA

  1. LOCALITY

  1. TOWN

  1. DISTRICT

  1. STATE

  1. PINCODE

  1. EMAIL

  1. MOBILE

  1. ACTOTAL COUNT TYPE

  1. PLAN


GST DATA BASE

Total Count: 25 Lakhs

Fields:

  1. Company name

  1. Address

  1. City

  1. State

  1. Mail ID

  1. Mobile number

  1. Mobile No 2

  1. Mob 3

  1. type

  1. turnover

  1. GST Number


RTO DATA

Total Count: 10 Lakhs

Fields:

  1. name

  1. owner num

  1. owner address

  1. owner email Id

  1. Src

  1. App Version

  1. Device Id

  1. Rto city

  1. Mobile

  1. color

  1. chasis No

  1. cc

  1. engine No

  1. src_mode

  1. model

  1. fuelType

  1. class

  1. r Date

  1. created At

  1. state


CRED  APP Database

Total Count: 3 Lakhs

Fields:

  1. AGREEMENT ID

  1. CUSTOMERID

  1. CRN

  1. APPCOAPPTYPE

  1. HOLDERNO

  1. INDV_CORPFLAG

  1. Customer Name

  1. Co Applicant Details

  1. TITLE

  1. DATEOFBIRTH

  1. GENDER

  1. MARITAL_STATUS

  1. PAN_NO

  1. ADDRESSTYPE1

  1. MAILINGADDRESS1

  1. MAILINGCITY

  1. MAILING STATE

  1. MAILING ZIPCODE

  1. MAILING PHONE1

  1. MAILINGE MAIL

  1. SCHEME

  1. CKYC_NO

  1. KYCPLACEOFDECLARATION

  1. Remark


POLICY BAZAR

Total Count: 7.8 Lakhs

Fields:

  1. Name

  1. Email

  1. Mobile

  1. City

  1. SUM INSURED

  1. PLAN TYPE


AMAZON

Total Count: 10.2 Lakhs

FIELDS:

  1. Email

  1. Name

  1. City_Name

  1. Billing_Phone

  1. Category_Grouped

  1. Category

  1. Sub_category

  1. Product_Gender

  1. Segment

  1. Class

  1. Family

  1. Brand

  1. Brick

  1. Item_NM

  1. Color

  1. Size

  1. Sale_Flag

  1. Payment_Method

  1. coupon_money_effective

  1. Coupon_Percentage

  1. Quantity

  1. Cost_Price

  1. Item_Price

  1. Special_Price_effective

  1. paid_pr_effective

  1. Value_CM1

  1. Value_CM2

  1. Special_price

  1. Paid_pr


BOOK MY SHOW 

TOTAL COUNT: 53.5 Lakhs

FIELDS:

  1. BMS USER NAME

  1. ADDRESS1

  1. ADDRESS2

  1. ADDRESS3

  1. DISTRICT

  1. STATE

  1. BMS ID

  1. TRANSATION TYPE

  1. MOBILE

  1. EMAILID


INSTAGRAM

TOTAL COUNT: 9.4 lakhs

FIELDS:

  1. Resume ID 

  1. Name 

  1. Mobile 

  1. Mobile 2

  1. Contact 

  1. City 

  1. Education 

  1. Designation

  1. Company 

  1. Salary 

  1. Experience

  1. Skills

  1. Preferred Location 

  1. Nationality 

  1. Industry

  1. passing Univercity College

  1. Date of Birth

  1. Gender

BETTING APPS:


CASINO (RAJBETS)

Total count: 38654

Fields:

  1. user_

  1. doc_

  1. id_

  1. source_

  1. id_

  1. email

  1. username

  1. first_name

  1. last_name

  1. number

  1. Total Country

  1. city


DREAM 11

Total count: 4.58 lakhs

Fields:

  1. MEMBER NAME

  1. EMAIL

  1. WINNINGS

  1. ENTRY FEE

  1. TEAMS

  1. POINTS

  1. AREA

  1. LOCALITY

  1. TOWN

  1. DISTRICT

  1. STATE

  1. MOBILE

  1. EMAIL


MPL

Total count: 5.08 lakhs

Fields:

  1. IP ID

  1. Data Entred

  1. Assigned Id

  1. Sourse

  1. User Id

  1. Currency

  1. Affilicate Code

  1. Member Id

  1. Add Code

  1. Id

  1. Name

  1. Mobile

  1. City

  1. Email Id

  1. Proff_Id

  1. Applied

  1. PAN Id


BIG BASKET

Total Count: 294040

Fields

  1. created_on

  1. updated_on

  1. created_by_id

  1. updated_by_id

  1. email

  1. password

  1. first_name

  1. last_name

  1. dob

  1. photo

  1. is_staff

  1. is_active

  1. is_superuser

  1. last_login

  1. registered_ip

  1. last_logged_ip

  1. date_joined

  1. hub_id

  1. address2

  1. zipcode

  1. location

  1. mobile_no

  1. phone_no

  1. activation_key

  1. oac_code

  1. news_status

  1. about_us

  1. address1

  1. city

  1. is_mapped

  1. is_validated

  1. area

  1. is_cashback_eligible

  1. apin

  1. pin

  1. validated_email

  1. validated_mobile_no

  1. validated_address

  1. manual_override_hub

  1. member_type_id

  1. cookie_value

  1. week_id

  1. mapped_on

  1. residential_complex

  1. mapped_by_id

  1. landmark

  1. city_id

  1. last_order_id

  1. date_of_first_order

  1. date_of_last_order

  1. num_of_orders

  1. first_order_id

  1. maximum_order_delivered_value

  1. total_order_orig_value

  1. total_order_orig_num_items

  1. total_order_delivered_num_items

  1. total_order_invoice_value

  1. total_order_delivered_value

  1. maximum_order_invoice_value

  1. total_order_delivered_num_qty

  1. total_order_orig_num_qty

  1. email_domain

  1. credit

  1. total_store_brand_order_value

  1. channel

  1. total_fv_order_value

  1. last_fv_order_date

  1. last_meat_order_date

  1. last_store_brand_order_date

  1. total_meat_order_value

  1. source_id

  1. ref_id

  1. email2

  1. phone_no2

  1. password_changed_time

  1. is_mobile_no_validated

  1. is_email_validated


UPSTOX DATA

Total Count: 1.1 Lakhs

Fields

  1. EMAIL

  1. LAST UPDATE DATE

  1. last Login Date

  1. source:

  1. Mobile


ZOMATO

Total Count: 20 Lakh

Fields

  1. Zomota User Name

  1. City

  1. Email

  1. Mobile

  1. User Delivery Address

  1. Order Item 

  1. Order Restaurant


CBSE Students DATA (10th & 12th Class)

1. Total count- 30 Lakh

2. Fields of information

1

Name

2

S/o

3

Gendre

4

medium

5

subject

6

subject

7

subject

8

subject

10

Mobile number

11

school mail ID

12

State

13

City

14

Pincode

15

Address


BYJUS & VEDANTU Database 

1. Total count- 18 Lakh

2. Fields of information

1

FIRSTNAME

2

STUDENT INFO

3

PHONES

4

LOCATIONINFO


Students Database 

1. Total count- 2 Crore

2. Fields of information

1

Student Name

2

PARENT NAME

3

CITY

4

MOTHER NAME

5

SURNAME

6

MOBILE NO

7

EMAIL ID

8

PINCODE

10

DISTRICT

11

TALUKA


NEET Students Database 

1. Total count- 1.8 Lakh

2. Fields 

1

APPLICATION NUMBER

2

NAME

3

EMAIL

4

MOBILE NUMBER

5

LOCATION


9th & 10th Students Database 

1. Total count- 1.5 Crore

2. Fields 

1

STATE NAME

2

DISTNAME

3

BLKNAME

4

CLUNAME

5

VILNAME

6

SCHCD

7

SCHOOL NAME 

8

STUDENTNAME

10

FATHERNAME

11

MOTHERNAME

12

MOBILENUMBER


NRI Database 

1. Total count- 1.2 Lakh

2. Fields 

1

Name

2

Address Line1

3

Address Line2

4

Address Line3

5

Address Line4

6

Country

7

Postal Code

8

Phone1

10

Phone2

11

Fax

12

Email


Facebook And Instagram Groups Database 

1. Total count- 800

2. Fields 

1

GROUP URLs


Job Seekers Database

1. Total count- 40 Lakhs

2. Fields of information

1

NAME

2

MOBILE

3

EMAIL

4

ADDRESS

5

CITY

6

DOB

7

GENDER

8

FUNCTIONAL_AREA

9

AREA_OF_SPECIALIZATION

10

INDUSTRY

11

RESUME_TITLE

12

KEY_SKILLS

13

COMPANY

14

SALARY

15

WORK_EXPERIENCE

16

LEVEL

17

PREFERRED_LOCATION

18

COURSE(HIGHEST_EDUCATION)

19

SPECIALIZATION(HIGHEST_EDUCATION)

20

INSTITUTE(HIGHEST_EDUCATION)

21

COURSE(2ND_HIGHEST_EDUCATION)

22

SPECIALIZATION(2ND_HIGHEST_EDUCATION)

23

INSTITUTE(2ND_HIGHEST_EDUCATION)

24

RESUME_ID


Domain Whois Database

1. Total count- 3.47 crore

2. Fields of information

1

NUM

2

DOMAIN_NAME

3

QUERY_TIME

4

CREATE_DATE

5

UPDATE_DATE

6

EXPIRY_DATE

7

DOMAIN_REGISTRAR_ID

8

DOMAIN_REGISTRAR_NAME

9

DOMAIN_REGISTRAR_WHOIS

10

DOMAIN_REGISTRAR_URL

11

REGISTRANT_NAME

12

REGISTRANT_COMPANY

13

REGISTRANT_ADDRESS

14

REGISTRANT_CITY

15

REGISTRANT_STATE

16

REGISTRANT_ZIP

17

REGISTRANT_COUNTRY

18

REGISTRANT_EMAIL

19

REGISTRANT_PHONE

20

REGISTRANT_FAX

21

ADMINISTRATIVE_NAME

22

ADMINISTRATIVE_COMPANY

23

ADMINISTRATIVE_ADDRESS

24

ADMINISTRATIVE_CITY

25

ADMINISTRATIVE_STATE

26

ADMINISTRATIVE_ZIP

27

ADMINISTRATIVE_COUNTRY

28

ADMINISTRATIVE_EMAIL

29

ADMINISTRATIVE_PHONE

30

ADMINISTRATIVE_FAX

31

TECHNICAL_NAME

32

TECHNICAL_COMPANY

33

TECHNICAL_ADDRESS

34

TECHNICAL_CITY

35

TECHNICAL_STATE

36

TECHNICAL_ZIP

37

TECHNICAL_COUNTRY

38

TECHNICAL_EMAIL

39

TECHNICAL_PHONE

40

TECHNICAL_FAX

41

BILLING_NAME

42

BILLING_COMPANY

43

BILLING_ADDRESS

44

BILLING_CITY

45

BILLING_STATE

46

BILLING_ZIP

47

BILLING_COUNTRY

48

BILLING_EMAIL

49

BILLING_PHONE

50

BILLING_FAX

51

NAME_SERVER_1

52

NAME_SERVER_2

53

NAME_SERVER_3

54

NAME_SERVER_4

55

DOMAIN_STATUS_1

56

DOMAIN_STATUS_2

57

DOMAIN_STATUS_3

58

DOMAIN_STATUS_4


Schools, Colleges, Universities & Education 

1. Total count- 4.2 lakhs 

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY


Teachers Database

1. Total count- 5.7 lakhs 

2. Fields of information

1

TELEPHONE NO.

2

MOBILE NO.

3

DATE OF BIRTH 

4

EMAIL

5

WORK EXPERIENCE

6

CURRENT LOCATION 

7

CURRENT EMPLOYER

8

DESIGNATION

9

ANNUAL SALARY


Advocates & Lawyers

1. Total count- 1.64 lakhs 

2. Fields of information

1

NAME

2

COMPANY

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CATEGORY

8

WEBSITE

9

DESIGNATION

10

CITY


Agents

1. Total count- 28,000. 

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CATEGORY

8

WEBSITE

9

DESIGNATION

10

CITY


Apparel & Garments

1. Total count- 65,200. 

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

STATE


Architect & Interior Designers 

1. Total count- 65,000. 

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY


Beauty Parlour, Hair Cutting Saloons & SPA 

1. Total count- 70,000. 

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY


BPO Call Centre Employees

1. Total count- 2.6 lakhs. 

2. Fields of information

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

City

7

State

8

Category


Building Material & Requisites.

1. Total count- 15,500. 

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY


Business Analyst 

1. Total count- 25000

     2. Fields of information

1

NAME

2

EMAIL ID

3

MOBILE NO.

4

INDUSTRY

5

CITY

6

ADDRESS


Business Development & Sales Professionals 

1. Total count- 150000.

     2. Fields of information

1

NAME

2

EMAIL ID

3

MOBILE NO.

4

CATEGORY

5

CITY

6

ADDRESS


Cab Users

1. Total count- 1.84 lakhs.

     2. Fields of information

1

TIME

2

CAB TYPE

3

CHARGE DESCRIPTION

4

NAME

5

TIME

6

DAY

7

EMAIL IDS

8

CONTACT NO

9

ADDRESS

10

CITY

11

STATE


CBSE School Email IDs

1. Total count- 18000.

     2. Fields of information

        1. Email Id


Cell Phones & Accessories Shops

1. Total count- 13600.

     2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY


CEO, CFO, CTO, CMO    

1. Total count- 2 Lakhs..

2. Fields of information.

1

Name of the Company

2

Name

3

Email

4

Job Title

5

Dept

6

Address1

7

Address2

8

Address3

9

Address4

10

Address5

11

City

12

State

13

PIN

14

STD

15

LL1

16

Fax No 1


Channel Sales Persons Database

1. Total count- 50000.

     2. Fields of information

1

Company

2

Name

3

Mobile

4

Email

5

Address 

6

City

7

State


Chartered Account 

1. Total count- 42000.

     2. Fields of information

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

Pincode

7

City

8

Website

9

Category

10

State

.


Chemical Pharma Companies Database

1. Total count- 39000.

     2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

STATE


Chemists Data base

1. Total count- 1.23 lakhs.

     2. Fields of information

1

LEVEL3

2

STATE

3

CITY

4

CENTER NAME

5

ADDRESS

6

LOCALITY

7

SUB_LOCALITY

8

PINCODE

9

BUILDING_NAME

10

LANDMARKS

11

TELEPHONE1

12

TELEPHONE2

13

TELEPHONE3

14

TOLLFREENUMBER

15

MOBILE

16

MOBILE2

17

MOBILE3

18

EMAIL

19

EMAIL1

20

WEBSITE

21

PTC_NAME

22

EMAIL


Chief Managers

1. Total count- 20800.

     2. Fields of information

1

Company Name

2

Name

3

Designation

4

State

5

Email

6

Mobile

7

IndustryType


Civil Engineer 

1. Total count- 2.53 lakhs.

     2. Fields of information

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

City

7

State

8

Category


Club Mahindra 326183

1. Total count- 3.26 lakhs.

     2. Fields of information

1

Mobile

2

Name 

3

Postal Address 

4

Current Employer 

5

Email

6

Contract Status

7

Product Owned

8

Season Owned

9

Channel


Commercial & Residential Properties

1. Total count- 29000.

     2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

SUB CATEGORY 


Company MD, Secretatiaty & Chairmen Database

1. Total count- 5.2 Lakhs.

     2. Fields of information

1

COMPANY NAME

2

NAME

3

DESIGNATION

4

STATE

5

EMAIL

6

MOBILENO

7

INDUSTRYTYPE


Company Proprietors Database

1. Total count- 3.9 Lakhs.

     2. Fields of information

1

COMPANY NAME

2

NAME

3

DESIGNATION

4

STATE

5

EMAIL

6

MOBILENO

7

INDUSTRYTYPE


Computer Laptop Dealers Database

1. Total count- 17000.

     2. Fields of information

1

COMPANY NAME

2

NAME

3

MOBILE 

4

STATE

5

EMAIL

6

CATEGORY


Computer, IT & Telecom Services

1. Total count- 54000.

     2. Fields of information

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

Pincode

7

City

8

Website

9

Category

10

Sub Category 


Consultants & Consulting Services Database

1. Total count- 2.04 Lakhs.

     2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

SUB CATEGORY 


Contractors Database

1. Total count- 10900.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

SUB CATEGORY 


Credit Card Holders 98 lakhs.

1. Total count- 98 lakhs.

2. Fields of information

1

BANK CODE 

2

ACTIVE /DEACTIVE

3

LEVEL

4

CONTROL NO

5

DR NO

6

NAME

7

MOBILE

8

ADDRESS

9

CITY

10

STATE

11

EMAIL

12

FIRST SWIPE  AMOUNT

13

SECOND SWIPE AMOUNT

14

INCOME DECLARED

15

PROFF 1

16

PROFF2

17

TYP OF AC

18

MOBILE ALERTS


CRM, Call Centres BPO Executives Database

1. Total count- 1.2 lakhs.

2. Fields of information

1

Name

2

Email Id

3

Date of Birth

4

Mobile No.

5

Functional Area

6

Area of Specialization

7

Industry

8

Resume Title

9

Key Skills

10

Current Location

11

Gender

12

Address


Dealers Database

1. Total count- 20,000.

2. Fields of information

1

ID

2

CAT_ID

3

COMPANY

4

NAME

5

LABEL

6

MOBILE

7

EMAIL

8

CITY

9

CAT1

10

CAT2

11

CAT3


Debit Card Holders.

1. Total count- 8.1 Lakhs.

2. Fields of information   

1

BANK CODE 

2

ACTIVE /DEACTIVE

3

LEVEL

4

CONTROL NO

5

DR NO

6

NAME

7

MOBILE

8

ADDRESS

9

CITY

10

STATE

11

EMAIL

12

FIRST SWIPE  AMOUNT

13

SECOND SWIPE AMOUNT

14

INCOME DECLARED

15

PROFF 1

16

PROFF2

17

TYP OF AC

18

MOBILE ALERTS


Defence Force Delhi NCR Database.

1. Total count- 2.55 Lakhs.

2. Fields of information

1

Name

2

Email Id

3

Government Force Name

4

Rank

5

Current Location

6

Address


Designers Database.

1. Total count- 50,000.

2. Fields of information

1

Company

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

STATE


Digital Photography Studios Database.

1. Total count- 58,000.

2. Fields of information

1

COMPANY 

2

NAME 

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE 

7

CITY 

8

CATEGORY


Dining Leisure Customers Database.

1. Total count- 24,000.

2. Fields of information

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

Pincode

7

City

8

Website

9

Category

10

Sub Category 


D-Mat Account Holders.

1. Total count- 35 lakhs.

2. Fields of information

1

CUSTOMERID

2

S2KID

3

NAME

4

MOBILE

5

EMAIL

6

TRADELOGINID

7

BRANCHID

8

CITY

9

COUNTRY


DTP Operators Database.

1. Total count- 14,000.

2. Fields of information

1

Name

2

Eail Id

3

City

4

Tele No

5

Mobile

6

Address


Economic Analysts Database.

1. Total count- 13,500.

2. Fields of information

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

Pincode

7

City

8

Website

9

Category

10

State


Educational Institutes Database

1. Total count- 11,100.

2. Fields of information

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

City

7

State

8

Category


Electricals Electronics Stores Database.

1. Total count- 1.5 Lakhs.

2. Fields of information


1

company

2

name

3

mobile

4

email

5

address

6

pincode

7

city

8

website

9

category

10

State


Employees Delhi NCR Bank Database.

1. Total count- 34000

2. Fields of information


1

SL NO

2

Name

3

FIRST_NAME

4

SECOND_NAME

5

COMPANY

6

Address

7

ADDRESS1

8

ADDRESS2

9

BILL_ADDRESS3

10

CITY

11

STATE

12

PIN_CODE

13

TELEPHONE_NO


Energy Power Sector Delhi NCR Database.

1. Total count- 23600.

2. Fields of information

1

SLNO

2

Name

3

FIRST_NAME

4

SECOND_NAME

5

BILL_COMPANY

6

Address

7

BILL_ADDRESS1

8

BILL_ADDRESS2

9

BILL_ADDRESS3

10

BILL_CITY

11

BILL_STATE

12

PIN_CODE

13

TELEPHONE_NO


Female Consumer Bangalore Database.

1. Total count- 1.17 Lakhs.

2. Fields of information

1

Name

2

Email Address

3

Region

4

Phone

5

Date of Birth

6

Gender


Financial Analysts Managers Industry Database.

1. Total count- 1.04 Lakhs.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

CITY

7

CATEGORY

8

STATE


Food Beverage Stores Database.

1. Total count- 31000.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

CATEGORY

9

STATE


Freelancers Data.

1. Total count- 76000.

2. Fields of information

1

NAME

2

EMAIL ADDRESS

3

MOBILE

4

INDUSTRY

5

CITY

6

ADDRESS


Frequent Flyer.

1. Total count- 18 Lakhs.

2. Fields of information

1

LOGIN NO

2

FLIGHTS

3

FLIGHTS/HOTELS

4

HOLIDAYS

5

ONE WAY

6

ROUND TRIP

7

GOING TO

8

DEPATURE

9

RETURN

10

TRAVELLER NO

11

CLASS

12

PASSENGER NAME

13

CITY

14

EMAIL ID

15

ADD-ONS

16

PAYMENT TYPE


Furniture Furnishing Business Database.

1. Total count- 27000.

2. Fields of information

1

COMPANY name

2

PTC _NAME

3

Mobile

4

Email

5

Address

6

PINCODE

7

City

8

Category

9

State


Gas Petroleum Database.

1. Total count- 1.03 lakhs.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

CITY

7

CATEGORY

8

STATE


Gems Jewellery Shops Database.

1. Total count- 34000.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

STATE


General Managers Database.

1. Total count- 14.6 Lakhs.

2. Fields of information

1

Name

2

Email Id

3

Mobile No.

4

Industry

5

Company

6

Level

7

Location

8

Edu.

9

Address


Government Employees.

1. Total count- 11 Lakhs.

2. Fields of information

1

NAME

2

MOBILE

3

EMAIL

4

ADDRESS

5

CITY

6

PINCODE

7

STATE

8

CATEGORY

9

DOB

10

GENDER


Graphic Designers Database.

1. Total count- 48000.

2. Fields of information

1

Name

2

Email Id

3

Mobile No.

4

Industry

5

Company

6

Level

7

Location

8

Education

9

Address


Gymnasiums

1. Total count- 24000.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

STATE


Health Beauty Shops Business Database 

1. Total count- 54000.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

SUB-CATEGORY


HNI & High Income Employee

1. Total count- 5 Lakhs.

2. Fields of information

1

Name

2

Email Id

3

Date of Birth

4

Mobile No.

5

Functional Area

6

Area of Specialization

7

Industry

8

Resume Title

9

Key Skills

10

Current Salary

11

Level

12

City

13

Gender

14

Address


Home, Garden Pets Suppliers Database.

1. Total count- 29000.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

CATEGORY

9

SUB-CATEGORY


Hotels, Restuarants, Restro Bars, Outlet.

1. Total count- 2 Lakhs

2. Fields of information

1

MASTER_ID

2

LOCATION_ID

3

COMPANY_NAME

4

STATE

5

CITY

6

PINCODE

7

LOCALITY

8

SUB_LOCALITY

9

ADDRESS

10

BUILDING_NAME

11

LANDMARKS

12

STDCODE

13

TELEPHONE1

14

TELEPHONE2

15

TELEPHONE3

16

MOBILE

17

MOBILE2

18

MOBILE3

19

LOCATIONEMAIL

20

LOCATIONEMAIL1

21

PTC_NAME

22

VALIDATED_REMARKS

23

LEVEL1

24

LEVEL2

25

LEVEL3

26

LEVEL3CODE


HR - Human Resources Database.

1. Total count- 38500.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

STATE


Importers Database.

1. Total count- 1.06 Lakhs.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

WEBSITE

9

CATEGORY

10

STATE


IT Companies Database.

1. Total count- 39000.

2. Fields of information

1

COMPANY NAME

2

NAME

3

DESIGNATION

4

STATE

5

EMAIL

6

MOBILE 

7

INDUSTRY TYPE


IT Professionals, Hardware Networking Working Employees Database.

1. Total count- 15 Lakhs.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

INDUSTRY 

9

STATE


Jewellers Database

1. Total count- 14800.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

PINCODE

7

CITY

8

INDUSTRY 


Lecturer Professor Database

1. Total count- 25000.

2. Fields of information

1

COMPANY

2

NAME

3

MOBILE

4

EMAIL

5

ADDRESS

6

CITY

7

CATEGORY 

8

STATE


Legal firms Database

  1. Total count: 11455

  2. Fields of Information: 

1

company name

2

city

3

pin code

4

Address

5

mobile

6

ptc_name

7

Company Email

8

Website


LIC Agents Database

  1. Total count: 10962

  2. Fields of Information: 

1

Email 

2

city


Logistic Management Database

  1. Total count: 87653

  2. Fields of Information: 

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

Pin code

7

City

8

Category

9

Sub Category


Industrial equipment Database

  1. Total count: 52,000

  2. Fields of Information: 

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

Pincode

7

City

8

Category

9

Sub Category


Males Database

  1. Total count: 22,00,000

  2. Fields of Information: 

1

name

2

email

3

mobile

4

city

5

gender

6

address

7

name


Manufactruing Database

  1. Total count: 162393

  2. Fields of Information: 

1

Company Name

2

Name

3

Designation

4

State

5

Email

6

Mobile No

7

Industry Type

Metals & Minerals Database

  1. Total count: 15850

  2. Fields of Information: 

1

company

2

name

3

mobile

4

email

5

address

6

pin code

7

city

8

website

9

category


MLM Leader Database

  1. Total count: 112675

  2. Fields of Information: 

1

Email


Mobile number Database

  1. Total count: 3,00,00,000

  2. Fields of Information: 

1

Click To Home

2

Order Number

3

Update the status

4

Idoc Status

5

Status

6

Service start date

7

Bill Plan

8

Lob

9

Cust Segment

10

Customeclass

11

Order Logged Date Time

12

Order Logged Date Time Chr

13

Si Number

14

Account Number

15

Customer Name

16

Sales Channel

17

Sales Channel Name

18

Billing Option

19

Co Name

20

Sim Number

21

Old Sim Number

22

Channel Name

23

Zone

24

SM

25

TM


NGO & Social services Database

  1. Total count: 22034

  2. Fields of Information: 

1

company name

2

ptc_name

3

mobile

4

Email

5

Address

6

pin code

7

city

8

Category


NRI (Non Resident Indian) Database

  1. Total count: 126633

  2. Fields of Information: 

1

Email

2

Name

3

Address

4

Address2

5

Address3

6

City

7

Coountry

8

Code

9

Phone

10

Fax


OLX Database

  1. Total count: 15,00,000

  2. Fields of Information: 

1

Name

2

Phone number

3

amount

4

city

5

state


PAN Card Holders Database

  1. Total count: 15,00,000

  2. Fields of Information: 

1

BANK CODE

2

ACTIVE /DEACTIVE

3

LEVEL

4

CONTROL NO

5

CC NO_L7

6

PAN

7

AC UPDATE

8

CARD HOLDER NAME

9

MOBILE NO

10

CITY

11

FIRM NAME

12

FIRST SWP  AMOUNT

13

CC ACTIVE DATE

14

ACTIVE TIME

15

SECOND SWP AMOUNT

16

INCOME DECLARED

17

EMAIL CONTACT

18

PROFF 1

19

PROFF2

20

TYP OF AC

21

MOBILE ALERTS

`

Photo Studio Database

  1. Total count: 28000

  2. Fields of Information: 

1

Business Name

2

Address

3

Area

4

City

5

Mobile 

6

Email

7

Website


Placement Agencies Database

  1. Total count: 48309

  2. Fields of Information: 

1

company

2

name

3

mobile

4

email

5

address

6

pincode

7

city

8

website

9

category

10

State


Policy Bazar Database

  1. Total count: 785333

  2. Fields of Information: 

1

Name

2

Email

3

Mobile

4

City

5

SUM INSURED

6

PLAN TYPE


Principals Database

  1. Total count: 14180

  2. Fields of Information: 

1

Company Name

2

Name

3

Designation

4

State

5

Email

6

Mobile No

7

Industry Type


Project leaders Database

  1. Total count: 43408

  2. Fields of Information: 

1

company name

2

ptc_name

3

mobile

4

Email

5

Address

6

pin code

7

city

8

Category

9

Sub-Category

10

State


Project leaders Database

  1. Total count: 32000

  2. Fields of Information: 

1

Company

2

Name

3

Mobile

4

Email

5

Address

6

City

7

Category

8

State


Property Dealers Database

  1. Total count: 15819

  2. Fields of Information: 

`1

email 

2

city 


Purchase & Procurement Heads Database

  1. Total count: 47125

  2. Fields of Information: 


1

Name of the Company

2

Name

3

Email

4

Job Title

5

Dept.

6

Address1

7

Address2

8

Address3

9

Address4

10

Address5

11

City

12

State

13

PIN

14

STD

15

LL1

16

LL2

17

Fax No 1

18

Industry Segment

19

Sub Industry Segment


Purchase Managers Database

  1. Total count: 67638

  2. Fields of Information: 

`1

Company 

2

Name 

3

Mobile 

4

Email

5

City 

6

Industry 

7

Address

8

Designation 


Real Estate Database

  1. Total count: 4,00,000

  2. Fields of Information: 

1

company name

2

city

3

pin code

4

locality

5

Sub Locality

6

Address

7

Building Name

8

Landmarks

9

StdCode

10

telephone1

11

telephone2

12

telephone3

13

mobile

14

Mobile2

15

Mobile3

16

Tollfreenumber

17

ptc_name

18

Email

19

Email1

20

CompanyEmail

21

Website

22

level1

23

level2

24

level3


Recruitment agencies Database

  1. Total count: 49904

  2. Fields of Information: 

`1

Company Name

2

Name

3

Mobile

4

Email

5

Address

6

pincode

7

City

8

Website

9

Category

Relationship Manager Database

  1. Total count: 43191

  2. Fields of Information: 

`1

company_name

2

ptc_name

3

mobile

4

Email

5

Address

6

pincode

7

city

8

Category


Religare Database

  1. Total count: 4,13,539

  2. Fields of Information: 

`1

DP ID No

2

Customer Name

3

Phone No

4

Mobile No

5

Customer Email ID

6

Email Reply

7

Address

8

City

9

State

10

Customer Bank A/C

11

Account Type

12

Date Of Brith

13

Proof of identity

14

Address Proof 

15

Type Of Account

16

Mobile Alerts

17

Sales Consultant


Retail Shops Database

  1. Total count: 35,000

  2. Fields of Information: 

1

Business Name

2

Street Address

3

Area

4

City

5

Phone1

6

Phone2

7

Email

8

Website

Samaj community wise Database

  1. Total count: 2,00,00,000

  2. Fields of Information: 

1

AppNo

2

CandidateName

3

FatherName

4

Gender

5

MobileNo

6

ResCategory

7

LocalArea

8

Minority

9

AddrHNo

10

AddrVillage

11

AddrCity

12

AddrDistrict

13

AddrPINCode

14

LandLine

15

EMail

16

HelpCentre

17

QuaExam

18

RegCent


Semi Government Database

  1. Total count: 19340

  2. Fields of Information: 

1

Company Name

2

Name

3

Designation

4

State

5

Email

6

MobileNo

7

IndustryType


Senior Citizens Database

  1. Total count: 10,60,000

  2. Fields of Information: 

1

Name

2

Mobile

3

Email ID

4

City

5

State

6

Gender

7

Date Of Birth

8

Year

9

Status

10

Address


Service Industry Database

  1. Total count: 18810

  2. Fields of Information: 

1

Company 

2

Name 

3

Mobile 

4

Email

5

Address

6

Pincode 

7

Category

8

City 


Shopping Database

  1. Total count: 81441

  2. Fields of Information: 

1

Company 

2

Name 

3

Mobile

4

Email

5

Address

6

Pincode 

7

City 

8

level1

9

level2

10

level3


Software Engineers Database

  1. Total count: 2,70,000

  2. Fields of Information: 

1

Name

2

Email

3

Mobile

4

Industery

5

Address


Steel Products Database

  1. Total count: 117329

  2. Fields of Information: 

1

Company 

2

Name 

3

Mobile

4

Email

5

Address

6

Pin code 

7

City 

8

State

9

Category 

Stock Broking & Trading Database

  1. Total count: 206817

  2. Fields of Information: 

1

company

2

name

3

mobile

4

email

5

address

6

pin code

7

city

8

website

9

category

10

State


Stock Traders Database

  1. Total count: 70000

  2. Fields of Information: 

1

ID

2

Contact Name

3

Business Name

4

Street Address

5

Area

6

City

7

PinCode

8

Phone1

9

Phone2

10

Phone3

11

Email

12

Website

For further details please contact:


Cyberabad DCP Crimes Shri Kalmeshwar Shigenavar, IPS.,


9490617204

Market Reports

Market Report & Surveys
IndianWeb2.com © all rights reserved